How I was able to Bypass XSS Protection on HackerOne's Private Program
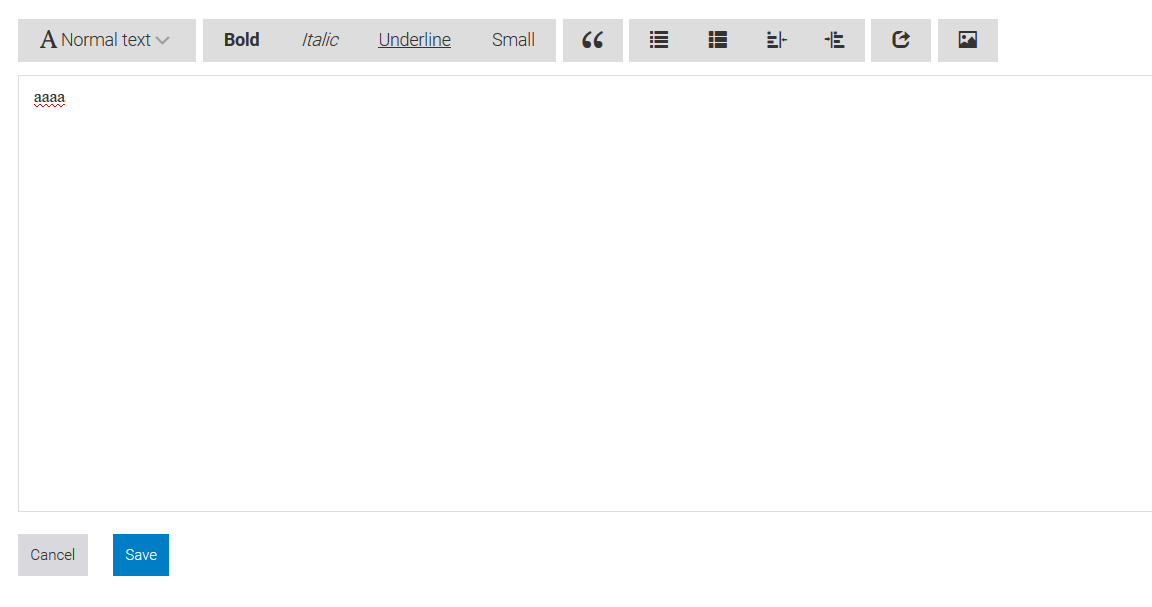
Hello friends, This is Jay Jani here and First of all frankly I would like to tell you all that I am completely a noob so I did some noobish things here. Please forgive me for my noobness. So, I was testing a private program on HackerOne and tried to find some basic vulnerabilities. There was a functionality where I can write a Post and Publish it on the internet. So i was looking for Cross Site Scripting bug there but application was a bit strong enough ( not fully :P ) to protect it. The Editor looks like:

I tried with basic paylods like “><svg/onload=confirm(1);> and all but failed. Then i noticed that application was removing all the payloads having “on” word like onerror, onload , basically event handlers.
Then I tried script alert(1); and the output:

I was like 
I quickly went through the post of my brother Armaan and the great Ak1t4 to get idea on how i could bypass this. Some of the payloads i used and the outputs I got are; <<script>alert(l); <>alert(l); <<scr<script>alert(1); alert(1);

<<scr<script>ipt>alert(1); ipt>alert(1);

<<scrip<script>t>alert(1); t>alert(1);

I was like 
The last Attack <<scrip<scriptT>alert(1); and Boom..!!


I know i did some noobish way to get alert but I am noob and just want to tell to the community that “There is always a way, you have to just try harder”.